Finally, it’s essential to understand that a load balancer is fundamentally not a safety product. For applications which have a corresponding deployment information it’s value studying that first as a few of them comprise product-specific DNS delegation steerage. This reduces the chance of the user’s request being directed to a server that’s unable to facilitate their request — resulting in downtime or an interrupted connection. Many of the DNS-based load balancing approaches are dynamic, which means that the load balancers consider server health and server response times when assigning requests.
Each method has its execs and cons, and the selection is dependent upon your specific necessities, technical expertise, and price range. Some content supply networks provide DNS-based load balancing as part of their providers. Now that you have High-speed VPS hosting in Ukraine got a thorough understanding of what DNS load balancing is, together with its advantages and limitations, it’s time to learn to truly do it. DNS caching is a elementary mechanism employed by purchasers and resolvers to retailer DNS responses regionally for a certain period. So we’ve established that DNS load balancing does not negatively affect search engine optimization, but that doesn’t imply that it’s all sunshine and rainbows.
Regular health checks and automated failover mechanisms are essential for reliability. Effective monitoring tools and management practices are crucial to making sure the health and performance of servers in a DNS load balancing setup. Some DNS resolvers cache IP addresses for a specific period (TTL), doubtlessly directing traffic to a much less optimal server until the cache expires.
Our Restore Providers Include:
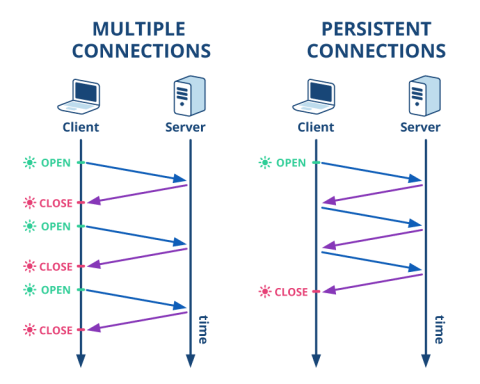
Conventional DNS load balancing does not embody built-in health checks, which means it cannot detect server failures or efficiency issues in real time. DNS load balancing is a method of distributing incoming site visitors across multiple servers by leveraging the Domain Name System (DNS). In today’s digital-first world, where users demand quick, reliable, and uninterrupted entry to net functions, the flexibility to effectively distribute site visitors across servers is crucial. DNS load balancing distributes incoming network site visitors across multiple servers by returning different IP addresses in DNS question responses. Advanced solutions fix these with health checks, weighted routing, and WebSocket support for real-time apps. UDP is a connectionless protocol, that means it would not set up a proper connection or 'handshake’ before sending data…
- Because most shoppers hook up with the first IP tackle within the list they receive, rotating the order effectively distributes connections across all servers over time.
- Selecting between DNS load balancing and hardware load balancing largely is determined by the precise needs and resources of your business.
- Do not skip health checks because round robin looks fine in testing.
- The client usually connects to the first IP it receives, so altering that order modifications which server will get the site visitors.
Developing A Technique For Community Modernization
Easy algorithms embrace random choice, round robin, or least connections. DNS load balancing is a strategic DNS management strategy that distributes incoming internet site visitors throughout multiple servers to optimize efficiency and forestall overloading any single server. As A Result Of most purchasers hook up with the primary IP handle in the list they obtain, rotating the order successfully distributes connections throughout all servers over time. Different purchasers obtain different addresses, spreading their connections throughout the out there pool of servers quite than sending all visitors to a single machine.